Company
ArcPoint Forensics
7 articles
 Hub Article
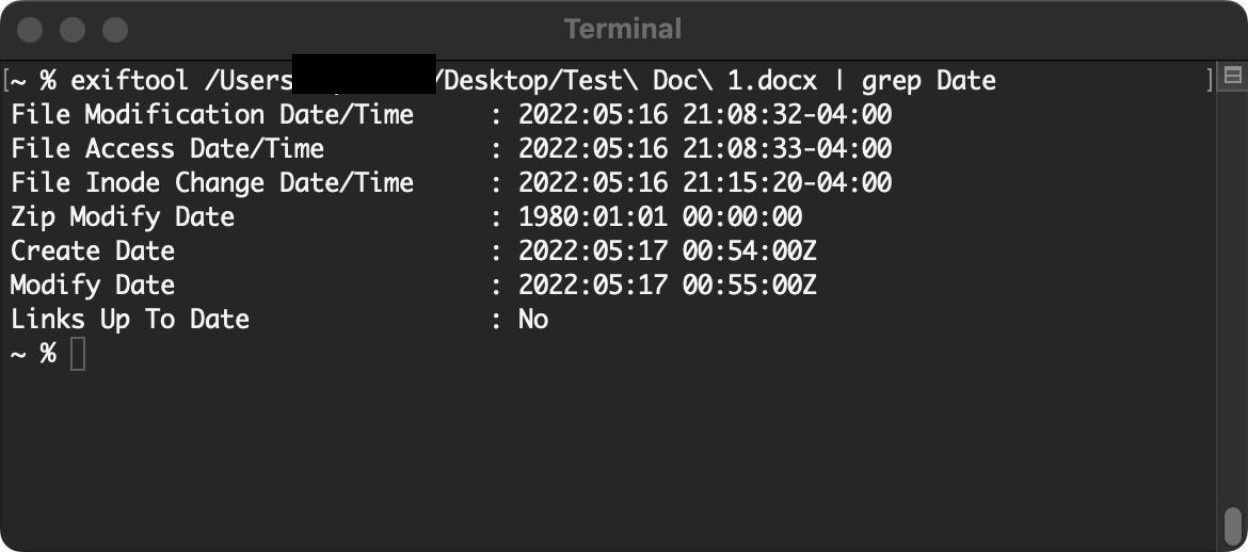
How to Use ExifTool to Look at Metadata
Today, we’ll discuss a very well known tool written by Phil Harvey. ExifTool is an extensively used tool to look at metadata from various types of files. It supports reading metadata from common file formats such as GPS, image files from many different digital cameras, video files, Microsoft Office files and many more. It’s freely available and can be downloaded from www.exiftool.org.
ArcPoint Forensics · Jun 20, 2022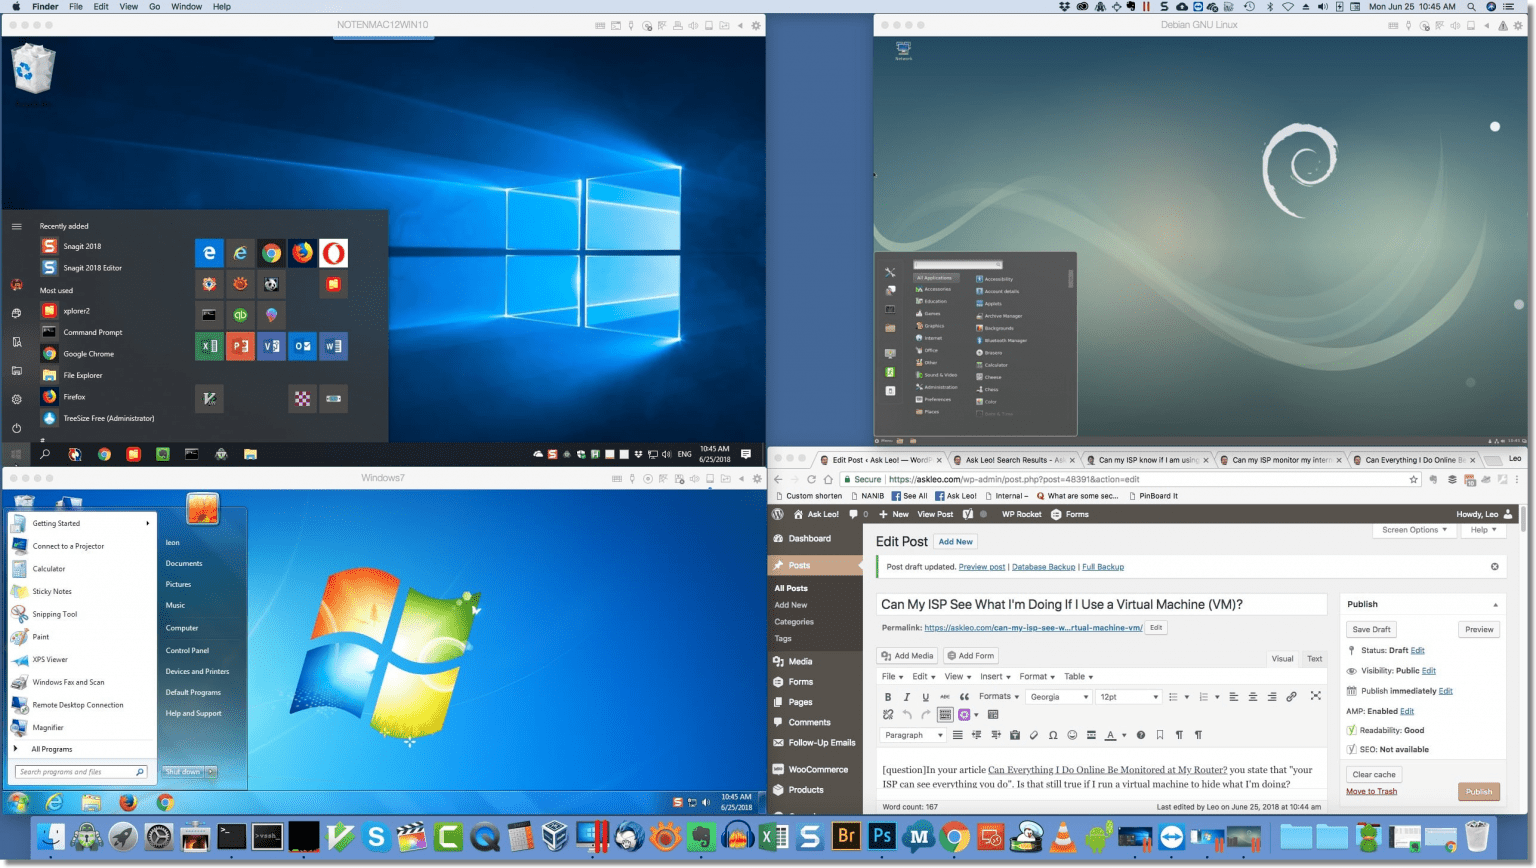 Hub Article
Working with Virtual Machines
Throughout the course of investigations, you run into individuals who have all types of technical backgrounds. For times when you have to look at evidence from a more technically savvy user, you may run into virtual machines installed on the machine. Virtual machines are separate instances of an operating system that you can run virtually.
ArcPoint Forensics · Feb 9, 2022 Hub Article
Rooting Microsoft Surface Duo
The Microsoft Surface Duo launched on September 10th, 2020. Instead of using Windows Phone OS, Microsoft decided to switch it up on everyone and introduced the Microsoft Surface Duo; a device that was built on Android
ArcPoint Forensics · Jan 14, 2022 Hub Article
Jailbreaking iOS Devices for Testing
When looking at digital evidence, forensic examiners want as much data as possible. This can be particularly tricky when working with an iOS device. Apple has these devices pretty locked down and can make it difficult to retrieve any data. If you have the passcode to the device, you can create a regular backup which will give you a lot of data.
ArcPoint Forensics · Nov 12, 2021 Hub Article
Installing Autopsy on macOS Big Sur
Many forensic examiners and investigators are used to having resources at their place of employment to work cases. We believe the learning process never stops and no one can be an expert in everything. Therefore we have to use the resources we have at our disposal and when we’re away from work, we may not have the computer forensic towers or dongles needed to run software. Autopsy is an open source forensic software that’s built on the Sleuthkit that is amazing for what it does at its price point (free).
ArcPoint Forensics · Nov 2, 2021 Hub Article
macOS Forensic Artifacts
It’s pretty much given that we live in a Windows-centric world. The majority of businesses and individual users out there use Windows machines to get work done. And because of that, it’s safe to say that the majority of incidents and forensic investigations target Windows machines. It leads many digital investigators to be well-versed in Windows forensics and know exactly where key artifacts are. But eventually, we all come across that MacBook Pro or iMac that we need to forensically examine.
ArcPoint Forensics · Oct 13, 2021 Hub Article
Speed Up the Digital Forensics Process
We’ve all been there, right? You’re a forensic examiner with a backlog of cases in your lab and you’ve just been handed another piece of media to add to your caseload. Of course, this is time sensitive too and the final report was needed yesterday. You want to get started with your examination right away but first you need to acquire an image of the evidence. You plug the new drive into a write-blocker and then into your forensic workstation and start the acquisition process to obtain a full forensic image you can work from.
ArcPoint Forensics · Sep 30, 2021