Tag
#iOS
6 articles
 Hub Article
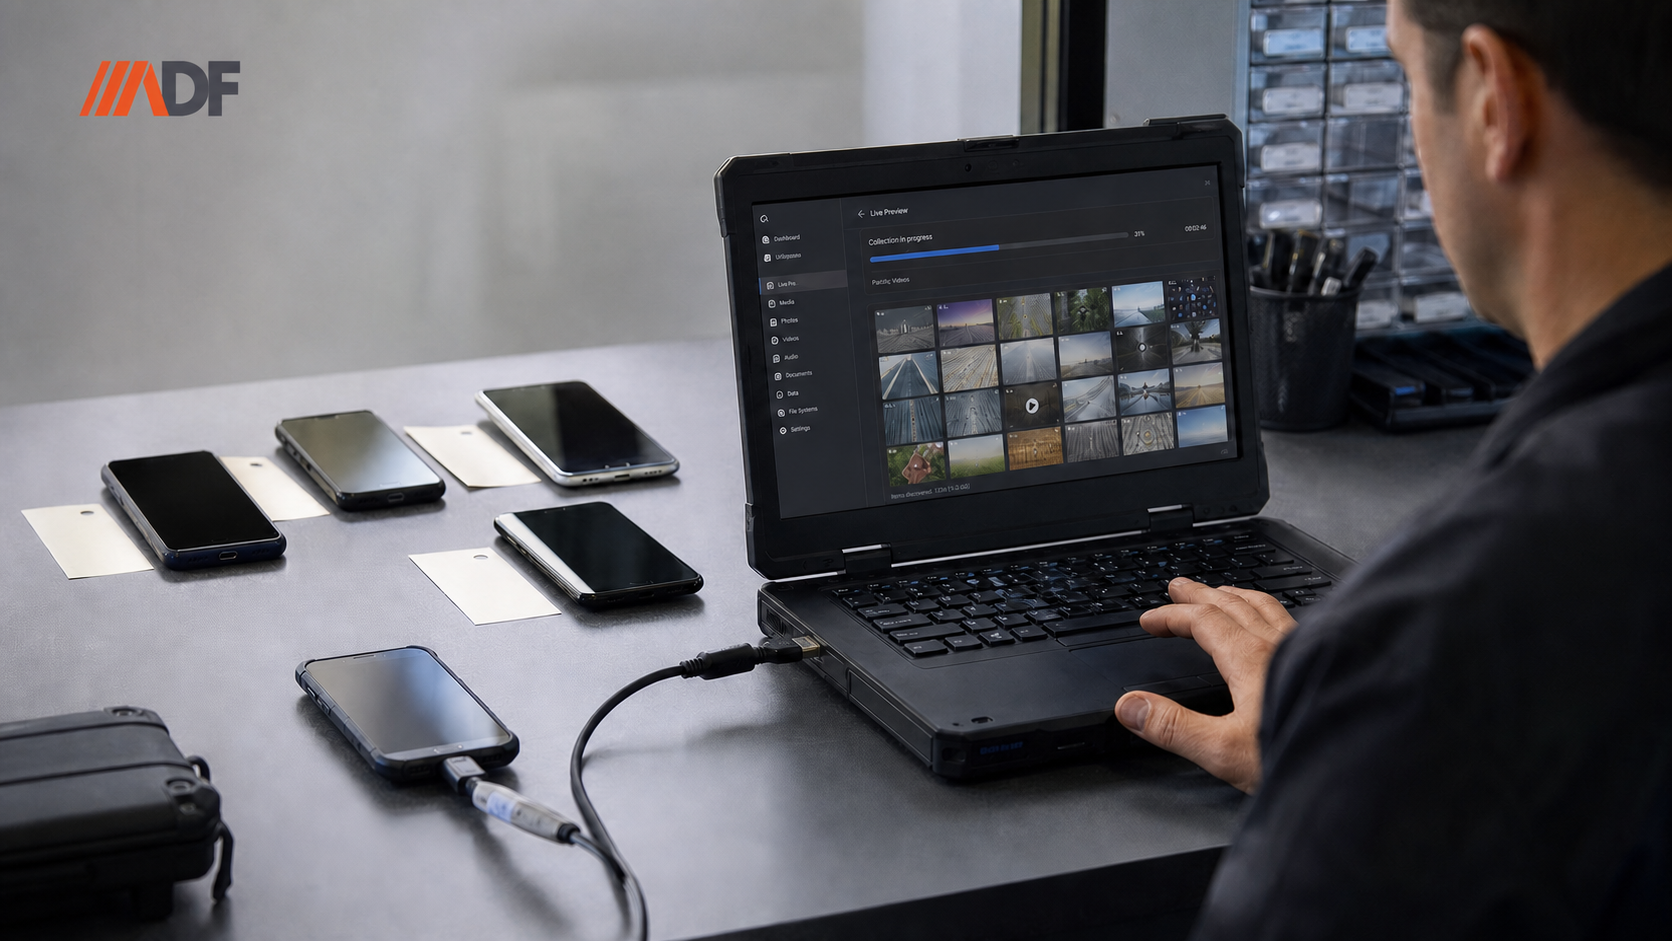
Before You Acquire Everything: On-Scene Device Triage with Preview Mode
ADF PRO Preview Mode lets examiners review mobile data while collection is still underway—helping teams make faster on-scene decisions, prioritize relevant devices, and reduce forensic backlogs.
ADF Solutions · Sep 3, 2026 Hub Article
Deleted Doesn’t Mean Gone: What 2026 Research Reveals About Mobile Anti-Forensics
Mobile anti-forensics can make evidence harder to see without fully removing it. A major 2026 review identifies where residual traces persist—and how examiners can build a more complete, defensible analysis.
Kevin DeLong · Aug 22, 2026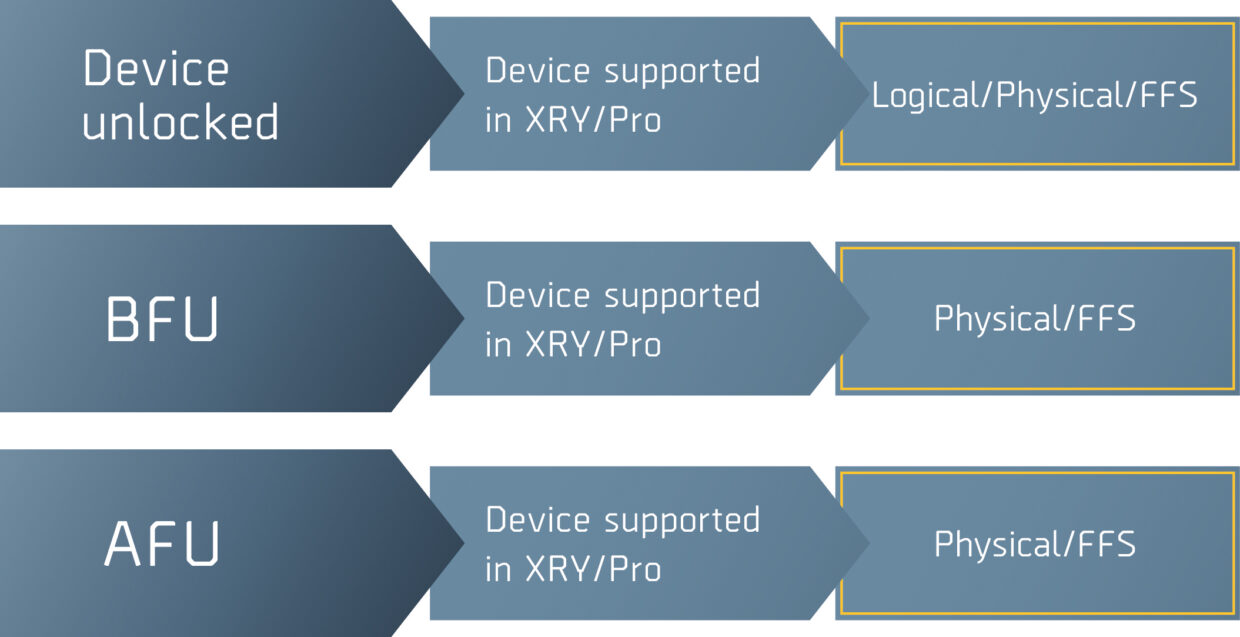 Hub Article
BFU – Seeing is Believing
This is the common reaction; a device needs extracting, and you find it in a BFU state. According to other vendors, your options are now limited. Even if you do get an extraction, it will only acquire basic information. BFU means the data is encrypted and secured.
Adam Firman · Dec 18, 2023 Hub Article
Jailbreaking iOS Devices for Testing
When looking at digital evidence, forensic examiners want as much data as possible. This can be particularly tricky when working with an iOS device. Apple has these devices pretty locked down and can make it difficult to retrieve any data. If you have the passcode to the device, you can create a regular backup which will give you a lot of data.
ArcPoint Forensics · Nov 12, 2021 Hub Article
Signal App Decryption
Signal is widely considered to be one of the most secure messaging services. Even Edward Snowden called Signal his favorite messenger app.
Belkasoft · Sep 13, 2021 Hub Article
Crack Encrypted iOS Backup Files
Learn to crack iOS backup files with Hashcat!
Kevin DeLong · Mar 1, 2020